If you can open website but import URL fails in the WYSIWYG HTML editor, the page itself is usually fine. Opening a page is a navigation that your browser performs for you. Importing it means the editor’s JavaScript must request the HTML and then read the response, and browsers only allow that across origins when the remote server grants permission through CORS (Cross-Origin Resource Sharing). Without that permission, the request can show up in the Network panel while its body stays unreadable to the editor.
The input is a page address, the expected output is that page’s HTML inside the editor, and the practical workaround is to save the HTML to your device and use Import File instead. Below I show how to tell a CORS block from a Content Security Policy block or mixed content, and what a saved copy will and will not contain. The platform rules were checked against MDN documentation and the editor’s homepage on November 9, 2026.
Table of Contents
Why You Can Open a Website but Import URL Fails
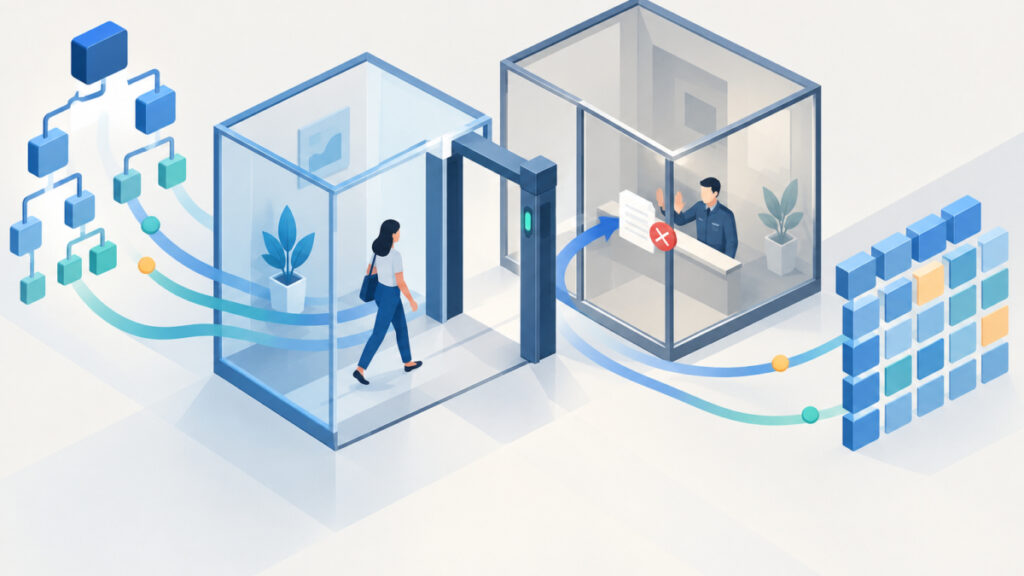
Typing an address into the tab bar is a top-level navigation. The browser downloads the document and renders it, and no page script ever receives the raw bytes. A script is different. Code running on the editor’s page that asks for a document on another site makes a cross-origin request, and the same-origin policy decides whether that code may read what comes back.
An origin is the combination of scheme, hostname and port. https://example.com and https://www.example.com are different origins, and so are the http and https versions of one host. Any site other than the editor’s own address is cross-origin from the editor’s point of view. MDN describes this in its same-origin policy reference.
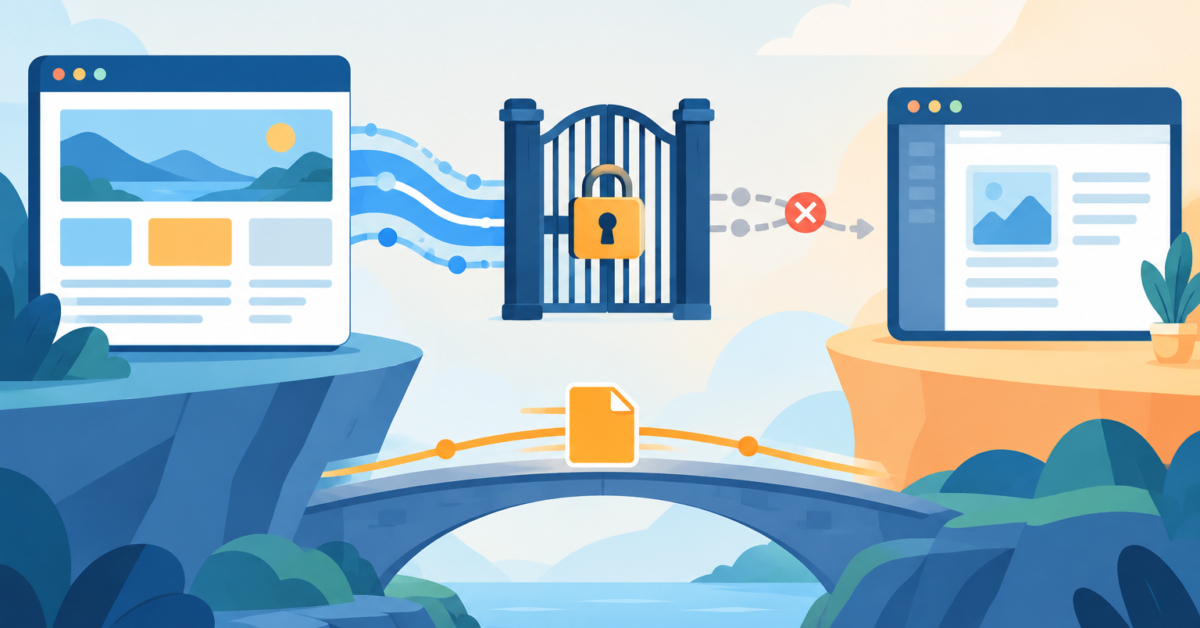
CORS is the mechanism the remote server uses to opt in. It answers with headers such as Access-Control-Allow-Origin that name the origin allowed to read the response. If that header is missing or names a different origin, the browser withholds the response from the script. CORS is not a ban on visiting a page, and the remote server may well have sent the full document. The browser simply refuses to hand it to the code that asked. The MDN CORS guide covers the full model.
The editor’s URL import fetches from the browser, so these rules apply to it like any other web page. I cannot change another site’s response headers from inside an editor, and a page cannot override the browser’s decision either.
One detail trips people up. Even a plain cross-origin GET needs permission before its response can be read. A preflight request (an automatic OPTIONS check) is only sent for requests that need one, such as those with certain custom headers or methods. Seeing no preflight in the Network panel does not mean the import was allowed.
When You Can Open a Website but Import URL Fails: Read the Console
Guessing wastes time because several different blocks produce a failed import. Reproduce the failure with developer tools open and let the browser state the reason.
- Open your browser’s developer tools (F12 in most desktop browsers) and select the Console and Network tabs.
- In the editor, choose Import URL and enter the address you can open normally.
- Read the Console message first. It usually names the exact policy that blocked the request.
- In Network, select the request and note its status, any redirects and the response headers, especially
Access-Control-Allow-Origin.
Then match what you see to the table.
| What you see | Likely cause | Who can change it |
|---|---|---|
No Access-Control-Allow-Origin header, or an origin that does not match the editor | The remote server’s CORS policy | The owner of the remote site |
A message naming Content Security Policy or connect-src | A restriction on connections the editor page may start | The owner of the page that sends the policy |
Blocked as mixed content when importing an http:// address | A secure page requesting an insecure resource | You, if the site also offers an https:// address |
| Reason: CORS request did not succeed | A network, TLS, DNS or extension problem, not necessarily a missing header | You, by checking connectivity, the certificate and any blocker |
A few cautions help you read these results. A 200 status in Network shows that the server responded, not that JavaScript was allowed to read the body. When a Content Security Policy has no connect-src directive, default-src can apply instead, as MDN explains in its connect-src reference. I am not claiming that the editor sets any particular policy, so let the Console text decide which row applies.
MDN also documents the specific wording of each failure on its CORS errors page, and the CORS request did not succeed entry is worth reading if the message mentions that phrase. For the mixed-content row, see MDN’s mixed content article.
Why no-cors and Browser Workarounds Do Not Help
When a request fails, mode: "no-cors" looks like an escape hatch. It is not one for importing. The request is sent, but the response is opaque: its body is hidden from your code. This fragment is for illustration only and should be run against a page you control.
const response = await fetch("https://example.com/page.html", { mode: "no-cors" });
console.log(response.type); // "opaque"
const html = await response.text();
console.log(html.length); // 0
The server may have sent the page, but your script receives an empty string. That is why no-cors cannot bring a remote page’s HTML into an editor.
I would also avoid launching a browser with its security checks disabled or installing an extension that rewrites headers just to get one import through. Those approaches weaken protection for every site you visit and are hard to keep scoped to one task. The save-then-import route below solves the same problem without touching browser security.
If you do control the remote server, the fix belongs there. The response needs to permit the editor’s origin, for example:
Access-Control-Allow-Origin: https://html-editor-online.com
Requests that send credentials such as cookies need additional compatible settings, and they cannot rely on the * wildcard value. If you do not control the server, no browser-side setting will make an unreadable response readable, so do not expect one.
Save the HTML, Then Use Import File
If you are allowed to use the page’s content, the dependable workaround is to take the network request out of the picture.
- Open the page normally in your browser and confirm that you have the right to reuse its content.
- Save the HTML to your device. Use your browser’s save-page command, or open the page source and copy it into a
.htmlfile. Menu names vary by browser. - In the editor, choose Import File and select the saved file.
- Check the result: headings, lists, links and images, comparing against the original page.
This works because a file you pick yourself is read through the browser’s File API, as described in MDN’s guide to using files from web applications. That is a different operation from fetching a document from another website, so the remote server’s CORS policy never comes into play. It is a way to work with a saved copy. It does not change what the remote server allows.
If you later export your edited result, remember that the downloaded HTML lacks the doctype, head and body wrapper that a complete page needs, so plan for that if the result is destined for a full document.
What a Saved Copy Does Not Contain
A saved file is a snapshot of source markup, not the live site. Expect these gaps:
- Styling and scripts that live in external files may not come with an HTML-only save.
- Images and fonts remain references to their original locations.
- Content behind a login is only present if your session produced it when you saved.
- Content generated by JavaScript after load may be missing, because saving the source does not necessarily capture the current rendered DOM.
The homepage editor is a rich-text editor built for content such as headings, lists, links, images and code blocks. It does not build full-page layouts or tables, and unsupported markup is removed on import. If you also edit in source view, note that source view removes class and ID attributes that the editor does not support. For editing full-page markup with a sandboxed live preview, the HTML Code Editor is the better fit, though it has no validator. If the saved file is minified and hard to read, the HTML Beautifier improves layout, but it does not repair invalid markup or restore removed comments.
Treat imported markup from any outside source as untrusted until you have read it. Do not run scripts you did not write, and review links and embedded media before reuse. The homepage also lists auto-save to the browser, so avoid importing confidential material on a shared device.
Who Can Fix Each Kind of Block
The cause tells you whose settings matter. A missing CORS permission belongs to the remote site, so a site owner can allow a specific origin on the responses that need it, while a visitor cannot. A Content Security Policy that restricts connections belongs to whoever serves the page that sent it. Mixed content is usually solved by using the secure address of the same resource. A network or extension failure is local to you.
If you have confirmed the Console shows something that looks like a bug in the editor itself, you can report it on the Contact page with the exact message text, but do not paste private addresses or credentials. In every other case the save-then-import route remains the practical option.
Frequently asked questions
Does CORS stop me from visiting a website?
No. CORS only controls whether a script on one origin can read a response from another origin. Opening a page in a tab is a navigation and is not affected.
Does a failed import mean the URL is wrong or the site is down?
Not necessarily. If the page opens normally in a tab, the address is probably fine. The Console message tells you whether the cause was a missing CORS permission, a Content Security Policy, mixed content or a network problem.
Can mode no-cors fix a blocked import?
No. A no-cors request returns an opaque response whose body your code cannot read, so you would get an empty result rather than the page’s HTML.
Why does Import File work when Import URL does not?
A file you select yourself is read through the browser’s File API. That does not make a cross-origin request, so the remote server’s CORS policy is not involved.
Does every cross-origin request send a preflight?
No. A preflight OPTIONS request is sent only for requests that require one. A simple GET may skip it but still needs permission to have its response read.
Who can change a CORS or Content Security Policy block?
The CORS response headers are set by the remote server, so only its owner can change them. A Content Security Policy is set by the page that sends it. As a visitor, you can use the saved-file workaround.
Is it safe to import any page I save?
Only import content you are allowed to reuse, and treat it as untrusted until you have reviewed it. Check links, embedded media and any markup before publishing, and never run scripts you did not write.
Next steps
When you can open website but import URL fails, the page is not broken and you are not banned. The browser is declining to let the editor’s code read a cross-origin response, or a policy or mixed-content rule is stopping the request first. Open developer tools, read the Console message, match it to the right row, and if you are allowed to use the content, save the HTML and choose Import File. Then check headings, links and images against the original before you build on the imported copy.
Related tools and resources on HTML Editor Online:
- WYSIWYG HTML Editor
- WYSIWYG HTML Download Missing Doctype, Head and Body: Why It Happens
- WYSIWYG Source View Removes Class and ID Attributes: Why and What to Do
- HTML Code Editor
Sources and further reading
- Cross-Origin Resource Sharing (CORS) – HTTP | MDN
- Content-Security-Policy: connect-src directive – HTTP | MDN
- CORS errors – HTTP | MDN
- Reason: CORS request did not succeed – HTTP | MDN
- Same-origin policy – Security | MDN
- Mixed content – Security | MDN
- Using files from web applications – Web APIs | MDN
- Advanced WYSIWYG HTML Editor – Create and Edit HTML Easily | HTML Editor Online